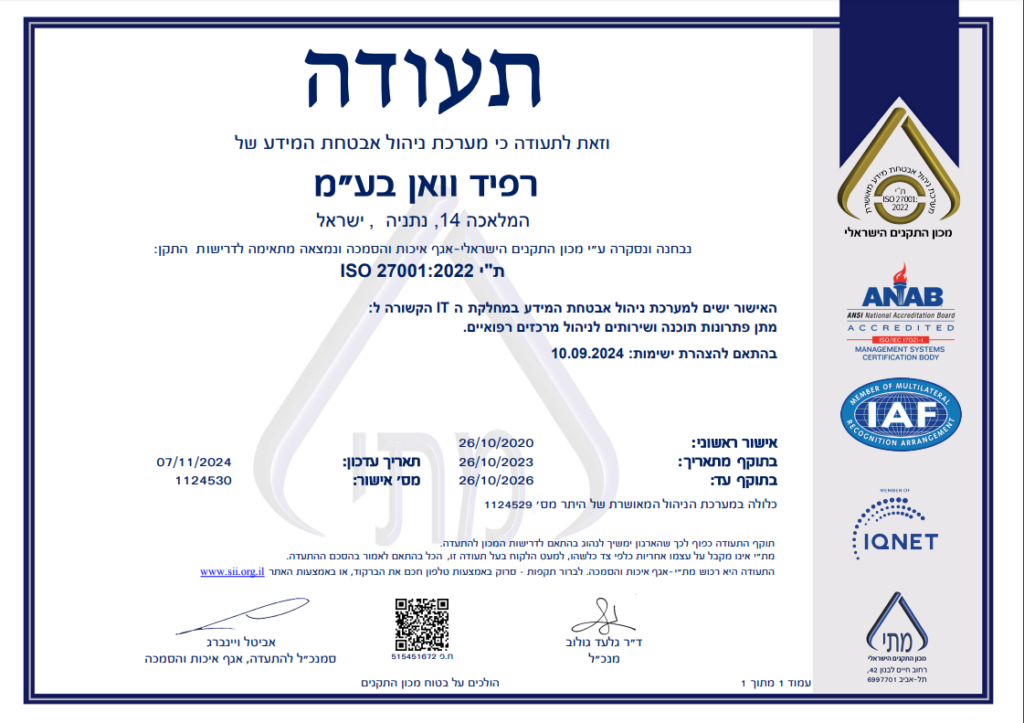
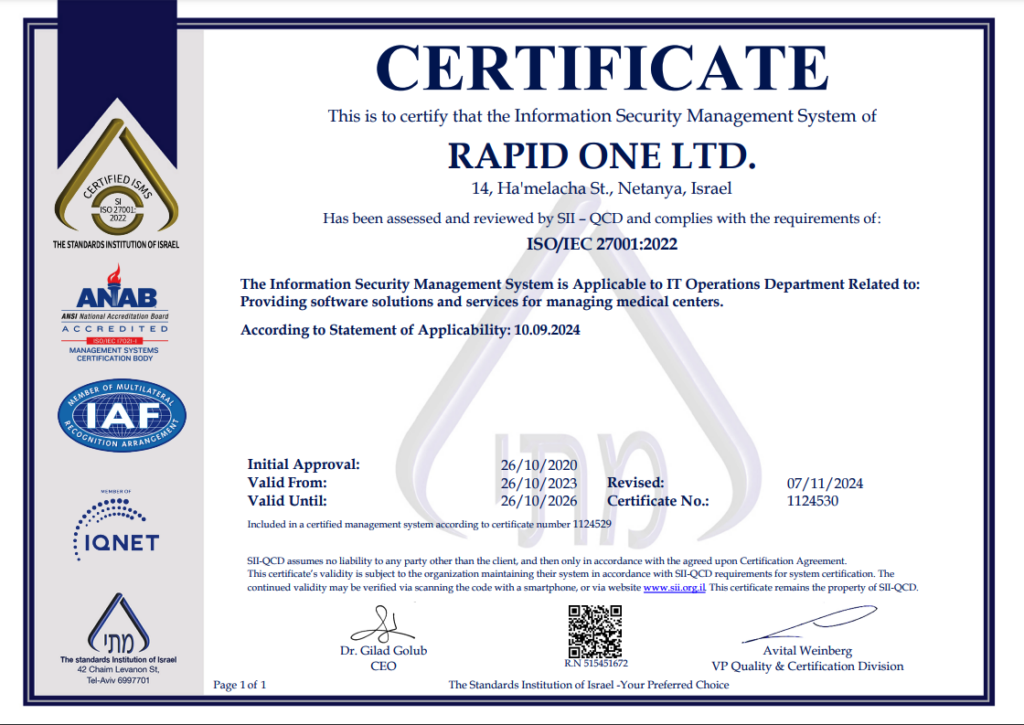
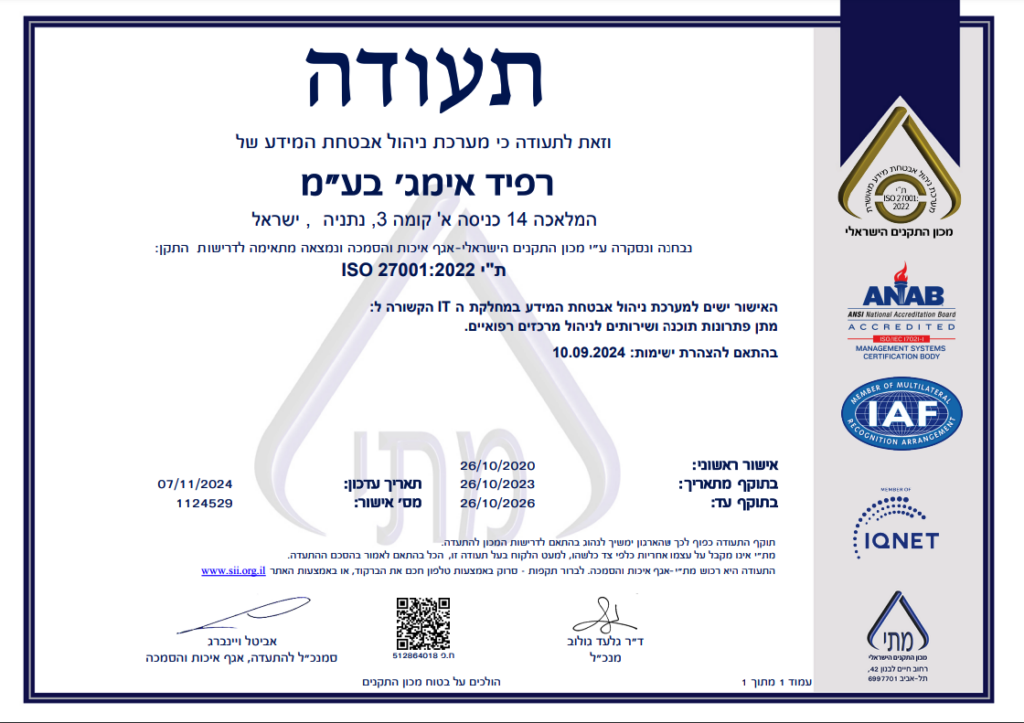
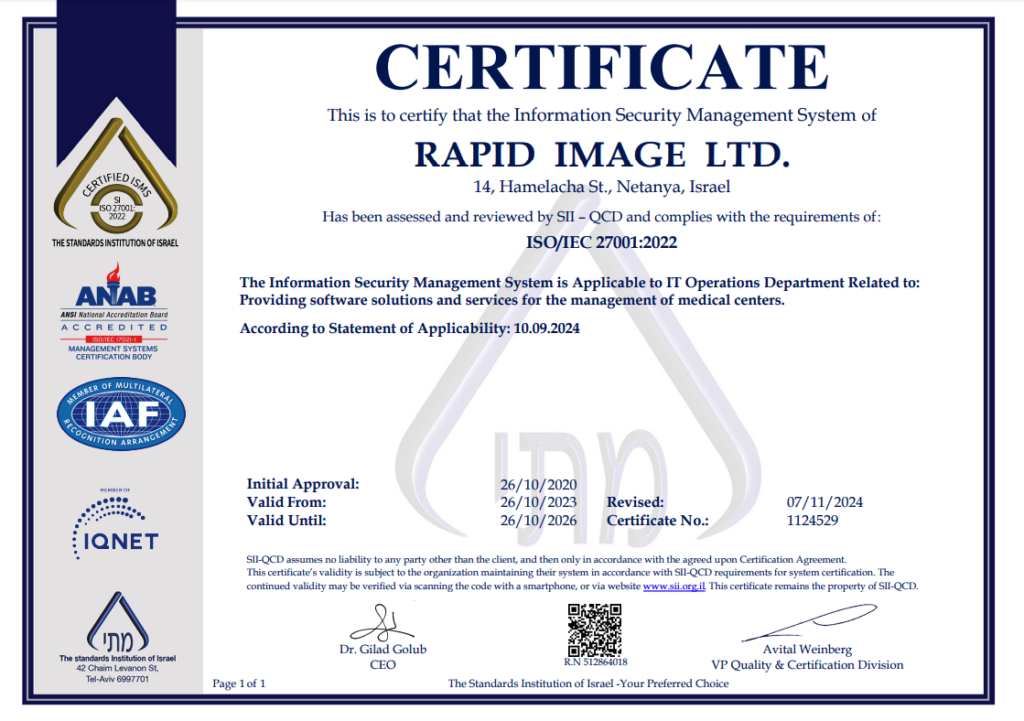
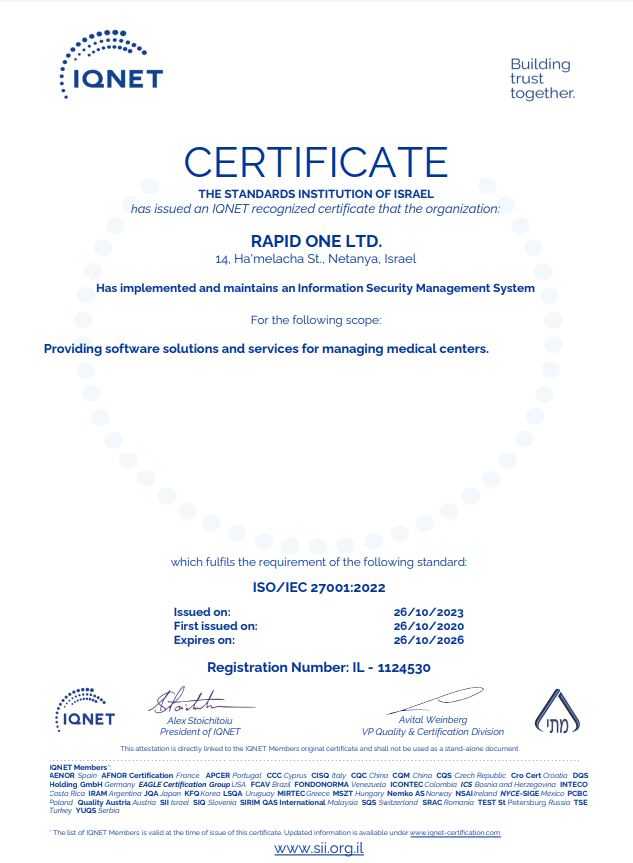
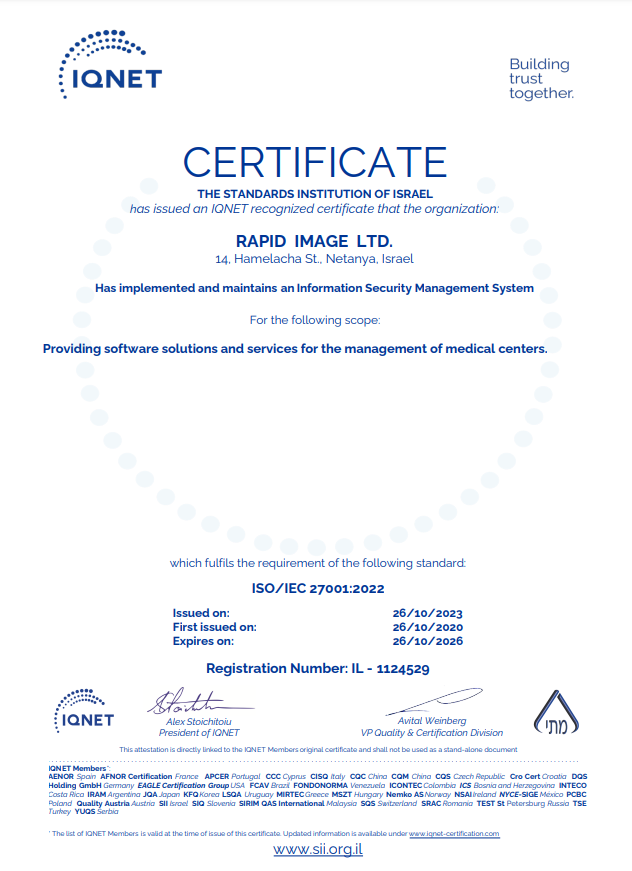
ISO 27001
Data Security Management
Sensitive Data Handling
ISO 27001:2013 standard is based on well-known ISO principles and includes familiar sections such as internal audits, management reviews, corrective and preventive actions, and document and record control.
Additionally, the standard requires conducting a risk assessment. It is necessary to register all of the organization’s information assets, identify potential risks, and establish a series of controls to mitigate these risks.
About ISO 27001
Protection against information system failures and information security is essential! Businesses and organizations can protect themselves from system malfunctions or misuse by investing in an independent audit of their information security management systems. The ISO 27001 standard involves a comprehensive examination and review of all information security aspects. From information loss, system intrusions, viruses, to e-commerce, unauthorized system access, and system recovery, ISO 27001 assesses the potential risks to your organization and highlights areas that require improvement. ISO 27001 sets a new standard for handling sensitive information. An information security management system has three main components:
1. Confidentiality – protecting essential information from exposure to unauthorized parties
2. Integrity – maintaining the accuracy and completeness of information and its processing
3. Availability – ensuring the availability of information and services as needed
An ISO 27001 certification provides assurance to your current and potential clients that your information security processes are defined and managed in a structured and systematic manner. The certification process helps you focus on the continuous improvement of information security, thus allowing for more reliable information exchange between you, your partners, and your clients.
The requirements of the standard
The standard is based on the well-known ISO principles and includes familiar sections such as internal audits, management reviews, corrective and preventive actions, and document and record control.
Additionally, the standard requires conducting a risk assessment. All of the organization’s information assets must be recorded, potential risks identified, and a series of controls established in order to minimize these risks.
The standard is intended for:
The standard is especially important for organizations that possess sensitive and confidential information, such as those in the fields of healthcare, law, security, and finance, as well as organizations that handle information that must always be available and reliable, and also those in commerce, supply, transportation, and more.
In other words, today, in the computer age, the standard is important for almost everyone.
זימון תורים אוטומטי ומדויק
המערכת מאפשרת למטופלים לבצע זימון תורים בצורה אוטומטית, עצמאית ונוחה, ללא צורך בהתערבות מצד הצוות. כל תור נקבע בהתאם לזמינות, מה שמבטיח שאין חפיפות או טעויות בתיאום. כך ניתן לייעל את הזמן של הצוות ולהפחית עומס מיותר על המוקדים.
תיאום גמיש ומתקדם
המערכת תומכת בזימון תורים עבור מגוון שירותים או טיפולים, ומספקת אפשרות לתיאום סדרת טיפולים לפי הצורך. כל תור מתעדכן בזמן אמת במערכת ומסונכרן באופן אוטומטי עם היומנים של הצוות, כך שנשמרת תמיד עקביות ונוחות.
תזכורות והתראות חכמות
עם שליחה אוטומטית של תזכורות לפני כל פגישה, המערכת עוזרת להוריד את שיעור הביטולים ומפשטת את התהליך עבור המטופלים. כך, הצוות יכול להתרכז בטיפול ובשירות מבלי לדאוג לניהול אקטיבי של התיאומים והזמנים.



The best software company in Israel, without a doubt. A dedicated, available, and professional team with a true understanding of the client's needs, full of wisdom, intelligence, and most importantly, heart.
Ben Or
Excellent software – very user-friendly both for managing calendars and for handling forms and patient tracking. In addition, I must mention that the technical support is amazing – there is a quick response to all questions, and they always provide solutions. Highly recommended!
Dr. Gal Michaeli-Geller
In the past decade, Rapid has been by my side every step of the way in my professional development. It is a very comprehensive software that provides me with all the tools I need to manage my clinic, from a lead management module, telephony, before-and-after image display, medical record management, business statistics, and of course, unified billing.
Dr. Shein
RapidOne is a cloud-based software that outperforms its competitors in many aspects (based on my experience). The software provides an excellent solution for almost everything a business needs: CRM for lead management, an excellent calendar for appointment scheduling, and of course, accounting management.
Michal Levin
Manager in the healthcare field
This is currently the most advanced software in Israel in Hebrew for managing a doctor's office. I switched to using the RapidOne system three years ago. The transition was relatively smooth and simple. I received a lot of support from the company both during the transition to the software and in the years that followed.
Eran Bar Meir
After reviewing several software options that we realized couldn’t meet all of our needs, we found Rapid. We are now, thank God, using Rapid for several businesses. It’s an excellent software that meets almost every requirement for our business—both for the practitioners and for office services, accounting, and more. Unlike other software we've seen, which are focused on a single business type (such as for practitioners only), Rapid is versatile and suitable for both practitioners and office management at the same time.
Oshrat Eldary
I would like to praise the professional and excellent work of the technical support team at Rapid, and especially the dedicated care and incredibly friendly attitude of the company employee, Slava.Beyond his unwavering professionalism, Slava brings patience, attentiveness, creative thinking, care, a genuine desire to help, and a big heart. Thank you and much appreciation for a wonderful service experience.
Eti Raz
Manager at "Harmony Center"
We are a private clinic that recently joined as a new client of RapidOne and would like to praise the excellent and efficient software, as well as the polite and fast service provided by the customer service, sales, and support departments who assisted us during the implementation and adaptation process. The training on the software was professional and patient. Thank you ❤️
Dr. Dayan Yosef